Complete Security Awareness Training: From Foundation to Armed
Table of Contents
Modern businesses face security threats that range from cyber attacks to physical violence. A complete security awareness training program tackles these risks directly. It prepares teams to spot, respond to, and reduce threats across the board. Whether you're protecting digital assets or physical property, the right training framework makes all the difference.
Security awareness training has evolved significantly. Organizations now know that protecting people and property takes more than basic rules.
It requires specialized skills, ongoing training, and a strong understanding of security principles.
It also calls for advanced tactics, such as armed security training.
Understanding Modern Security Awareness Programs
AI driven security awareness training program serves as your company's first line of defense. According to NIST Special Publication 800-50 Revision 1, effective programs use a lifecycle approach. It supports behavior change as part of risk management. The goal is to develop a security culture where every team member understands their role in maintaining safety.
Security awareness differs from training in important ways. Awareness focuses attention on security issues and helps people recognize threats. Training builds specific skills that allow personnel to perform security functions effectively. The most successful programs incorporate both elements.
Organizations should address awareness and training needs across all personnel, from front-line employees to executives. Everyone has responsibilities, and each role requires appropriate preparation.
The Five Core Components of Security Awareness Training
1. Understanding Roles and Responsibilities
Every security program starts with clarity about who does what. Agency heads must give security awareness high priority. Chief Information Officers and security program managers develop strategies and ensure adequate funding. Managers at all levels work to reduce errors by making sure their teams receive proper training.
Users—including employees, contractors, and visitors—must understand and comply with security policies. They need training in the specific rules of behavior for the systems and applications they access.
2. Building a Program Lifecycle
NIST identifies four critical steps in building an effective program:
- Design Phase: Conduct an agency-wide needs assessment and develop a training strategy. This strategic document identifies implementation tasks that support established security goals.
- Development Phase: Focus on training sources, scope, and training content development. Determine whether to build materials in-house or seek contractor assistance.
- Implementation Phase: Address effective communication and program rollout. Consider delivery options like web-based training, distance learning, video, or on-site instruction.
- Post-Implementation: Keep the program current and monitor its effectiveness using surveys, focus groups, and benchmarking.
3. Addressing Security Basics
Core security awareness topics typically include:
- Password security and verification
- Data backup procedures
- Virus protection and cyber security
- Physical security measures
- Incident reporting protocols
- Social engineering awareness
Training should use varied methods to match how people learn. Research shows that traditional "blocked training" gives lots of sensitive information in a short time. It often leads to poor long-term retention. Instead, distribute the training into shorter sessions over a longer period.
4. Adopting Industry Standards
ISO/IEC 27001:2022 Annex A Control 6.3 stresses the need for ongoing security awareness, education, and training programs. Organizations should ensure all personnel receive appropriate training and regularly update their knowledge.
The standard requires that training programs:
- Address specific organizational risks
- Cover relevant legal and regulatory requirements
- Include both security and privacy considerations
- Provide role-based instruction for personnel with specialized responsibilities
5. Measuring Program Effectiveness
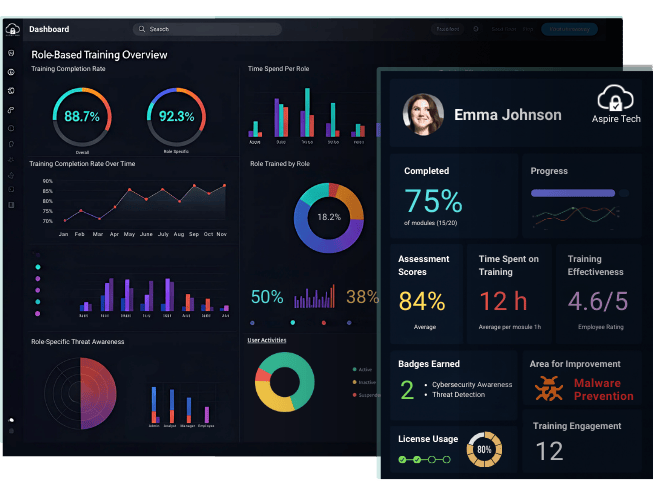
You can't improve what you don't measure. Effective programs include metrics and evaluation methods to regularly assess impact. Track completion rates, test scores, incident reduction, and behavioral changes. Use this data to refine your approach and demonstrate value to stakeholders.
When General Awareness Meets Specialized Armed Security Training
While comprehensive security awareness prepares all personnel for common emerging threats, certain roles and environments demand specialized skills. Armed security training is advanced security training. It prepares staff for high-risk situations where basic awareness is not enough.
Understanding Armed Guard vs. Private Security Officer Roles
A private security officer provides protective services through presence, observation, and reporting. They deter criminal activity and respond to incidents using non-lethal methods.
Armed security guards have added duties. They undergo training to handle firearms. They also know when deadly force may be legal and ethical.
Essential Armed Security Training Components
- Firearms Fundamentals: Weapon nomenclature, safety mechanisms, loading and discharging procedures, proper cleaning and maintenance.
- Use-of-Force Continuum: Understanding the five levels of force, from officer presence through lethal force.
- De-escalation techniques
- Scenario-Based Training
- Legal and Regulatory Compliance
- Emergency Response
Building Your Security Training Program: A Practical Roadmap
Step 1: Assess Your Security Needs
Step 2: Establish Clear Policies
Step 3: Select Training Providers
Step 4: Implement Mandatory Training
Step 5: Maintain Compliance
Step 6: Provide Ongoing Support
Compliance Considerations
Security training requirements vary by state and industry. Federal facilities must comply with FISMA requirements and OMB Circular A-130. Private sector organizations should align with ISO 27001 standards and industry-specific regulations.
The Bottom Line: Training as Investment, Not Expense
Security incidents cost organizations millions in losses, liability, and reputation damage. A complete security awareness training program is not just a compliance checkbox. A strategic investment in your company’s resilience. It can also include specialized armed security training when needed.
Research shows that well-trained staff make better decisions under pressure. They respond better to threats. They help create safer spaces for everyone. Whether you use basic security training or armed guard services, the core is the same.
Provide ongoing education, build practical skills, and commit to constant improvement. Organizations that prioritize security training report fewer incidents, lower insurance premiums, and stronger security cultures. More importantly, they protect the people and assets that matter most.
Stay Updated
Get the latest cybersecurity insights delivered to your inbox.
Related Articles